
Security Blog
Tutorial
19 articles in Tutorial.

What happens on the Darknet ?
Alpha bay, Silk Road, Hansa: They made the headlines of newspapers for weeks. They were underground markets offering several illicit goods and services and were shut down in 2013 and 2017. All were using Tor, currently the most used parallel Internet network, called Darknet. DARKNET Computers connec
How to Hack with Mimikatz: Tutorial
If you are a hacker, you probably already know about mimikatz. This tool is widely used by hackers to retrieve passwords. Learn how to use.
How to setup your malware honeypot (V2)
Catch malware with your own Honeypot – Learn how to deploy a honeypot in 10 minutes with this step by step guide about Cuckoo sandbox. Easy sandboxing.
Cuckoo Sandbox Customization (V2)
Get an anti-malware removal report with a very simple cuckoo sandbox customization. Learn how Cuckoo works and how to add custom modules.
Adlice PEViewer : Bring Analysis to the Next Level
Adlice PEViewer is a PE parsing tool helping you in your everyday malware analysis and debugging. Learn how it works and how amazing it can be.
Cuckoo Sandbox Customization
Get an anti-malware removal report with a very simple cuckoo sandbox customization. Learn how Cuckoo works and how to add custom modules.

Free Stack for Small Development Teams
FREE stack for small development teams. Get your own with Gitlab, Trello, Freshdesk and more, everything connected into the same Slack chat.
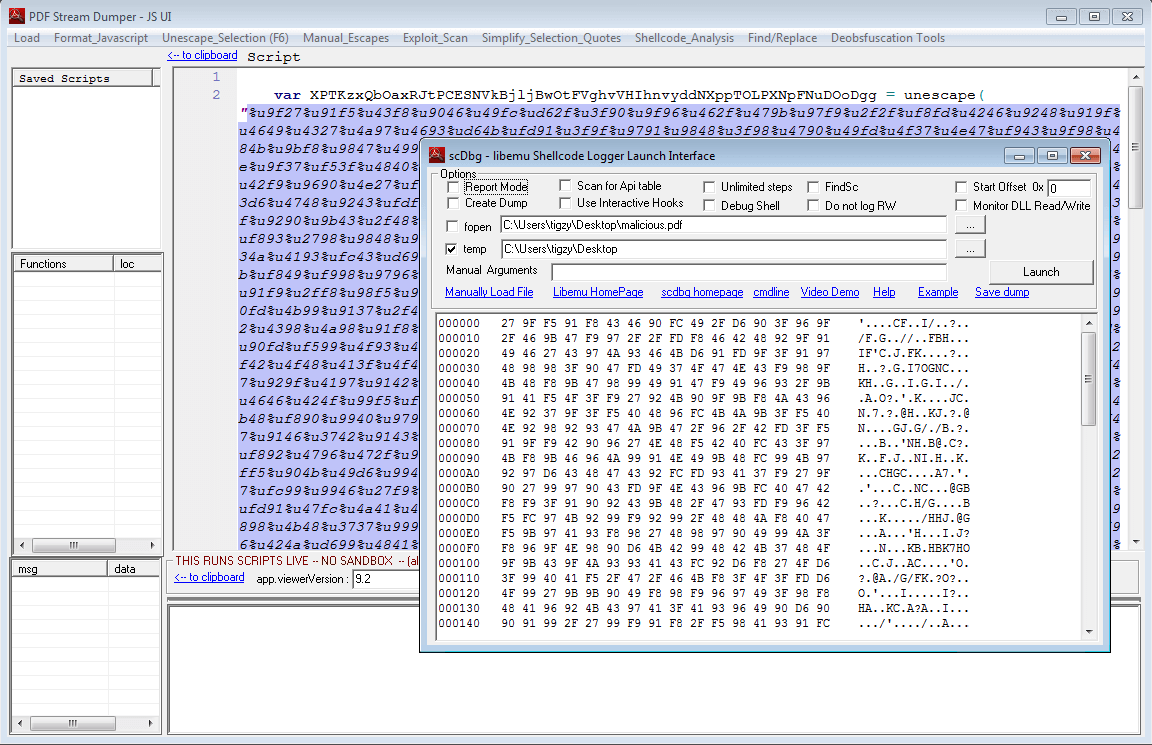
Infected PDF : How to Extract the payload ?
Infected PDF: Extract the payload – Infected PDFs have always been a popular way to infect computers, learn how it malicious PDF files are built.
Catch malware with your own Honeypot
Catch malware with your own Honeypot – Learn how to deploy a honeypot in 10 minutes with this step by step guide about Cuckoo sandbox. Easy sandboxing.

RunPE: How to hide code behind a legit process
RunPE: How to hide code behind a legit process – RunPE is a trick used by some malware to hide code into a legit process. Learn how to detect.
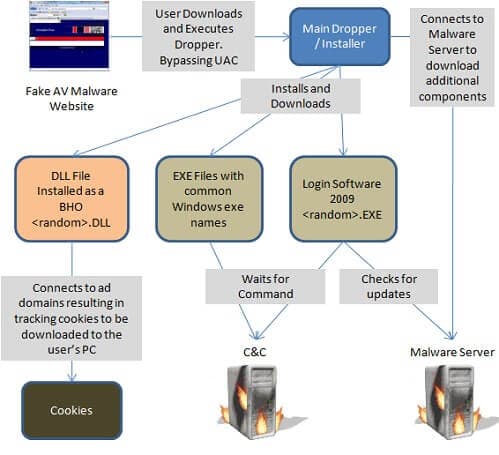
What’s a malware ? Definition of Virus, Adware, Spyware
This is a general explanation about different kind of online threats. What they do, and how. Introduction to viruses, malware, worms, adware and others.
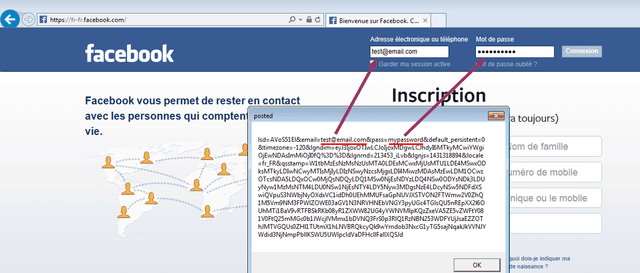
Internet Explorer BHO: A spy in your browser
Internet Explorer extensions (BHO) are a very stealth way to inject code in a web browser. Learn how it works to better prevent further infections.

Userland Rootkits: Part 1, IAT hooks
Userland Rootkits explained. This is the first part of this rootkit writing tutorial in which we will detail the basics about userland rootkits.
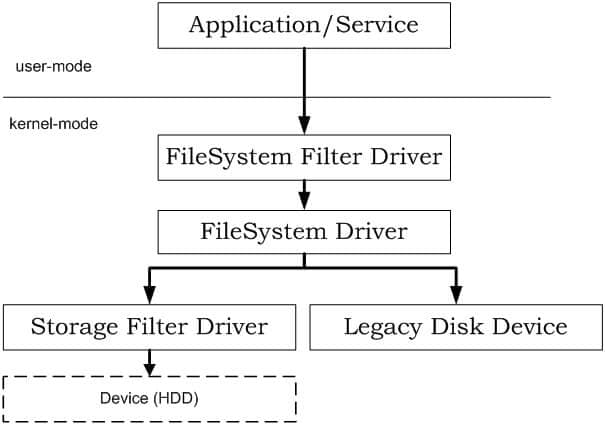
KernelMode Rootkits: Part 3, kernel filters
KernelMode Rootkits explained. This is the third part of this rootkit writing tutorial in which we will detail the basics about kernel rootkits.
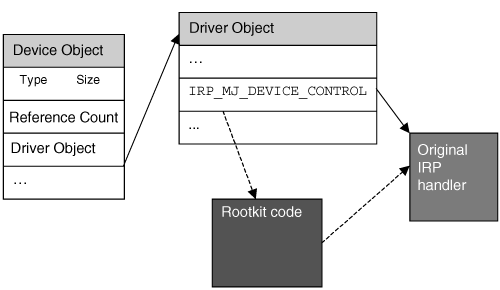
KernelMode Rootkits: Part 2, IRP hooks
KernelMode Rootkits explained. This is the second part of this rootkit writing tutorial in which we will detail the basics about kernel rootkits.
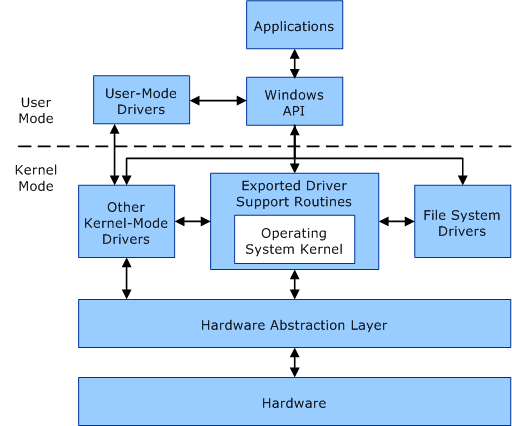
KernelMode Rootkits: Part 1, SSDT hooks
KernelMode Rootkits explained. This is the first part of this rootkit writing tutorial in which we will detail the basics about kernel rootkits.
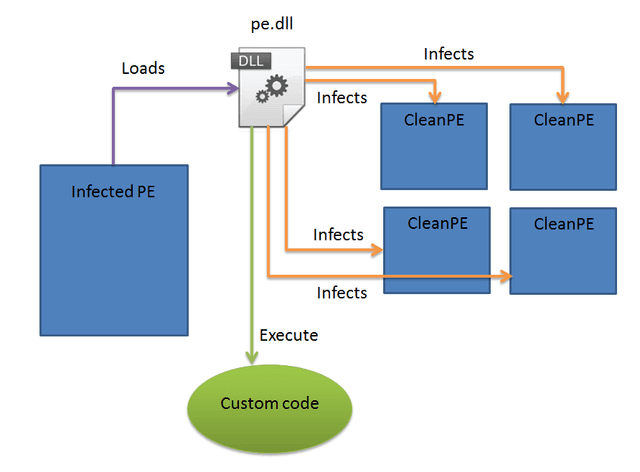
Chronicles of a PE Infector
Writing and Analysis of a portable executable (PE) infector. Educational tutorial on how to write your own PE infector that remains hidden in the system.
PE Smallest Executable
Learn how to modify a portable executable (pe) file to strip all the junk code and keep only the strict minimal bytes to keep it perfectly functional.
How to Make an antivirus engine
Learn the theory with code snippets on how making your own robust and reliable Antivirus / Anti-malware engine. Step by step guide.