
Security Blog
Analysis
27 articles in Analysis.

KMS Activators, Are They Malware?
Infections related to the use of hacktools like Windows Loader or KMSPico are rising. Learn how malware authors use them to spread cryptominers, ransomwares and ultimately take control of your newly installed operating system.
CCleaner Delivers Floxif Malware
Popular cleanup tool CCleaner was compromised to deliver the Floxif malware. Learn how this happened and find if you are at risk.
What is Code Signing?
Code signing is required to load drivers in Windows. Also, they tell users if an application can be trusted and launched. Learn how it works.
Macro malware, the biggest online threat
Macro malware are known for decades but still remain the preferred infection method for infecting machines with Ransomware, Trojans, … Learn how it works.

Exploits Explained, Exploit Kits (Part 3)
Discover exploitation methods, exploits development and inner workings and learn about the countermeasures that exists to protect your infrastructure.
Google Chrome: How to Bypass Secure Preferences
Google Chrome protects its user preferences using a hashing mechanism. However, there’s a way to bypass this, and it’s quite used by malware in the wild.
Fileless Malware using Powershell: Analysis & Removal
Fileless malware has always been popular and widely covered (Example: Poweliks). Study of a fileless malware stored in the task scheduler.
Exploits Monetizing, Exploit Kits (Part 2)
Discover the inner working of the places where transactions between exploits dealers take place and the conditions of such transactions.
RogueKiller, Inside WMI Scanner
Quick approach about Windows Management Instrumentation (WMI). Meet Adware Yeabests, hiding in the WMI and see how RogueKiller takes care of it.

Exploits Definition, Exploit Kits (Part 1)
Exploits and Exploit kits play a major role in the spread of malware. Learn how they work and how to protect yourself from such threats.

Ransomware : How to protect yourself against them
Ransomware became the threats of the web. Learn how they work, their effects, and how to protect yourself from such malware.
Infected PDF : How to Extract the payload ?
Infected PDF: Extract the payload – Infected PDFs have always been a popular way to infect computers, learn how it malicious PDF files are built.

RunPE: How to hide code behind a legit process
RunPE: How to hide code behind a legit process – RunPE is a trick used by some malware to hide code into a legit process. Learn how to detect.
BreakingNews PUP, Study of an aggressive rootkit
PUPs (for potentially unwanted programs) are harmless by design, most of the time. Here we will study a case where such program behaves like a rootkit.
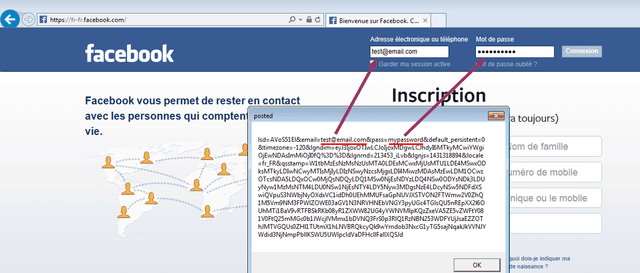
Internet Explorer BHO: A spy in your browser
Internet Explorer extensions (BHO) are a very stealth way to inject code in a web browser. Learn how it works to better prevent further infections.

Userland Rootkits: Part 1, IAT hooks
Userland Rootkits explained. This is the first part of this rootkit writing tutorial in which we will detail the basics about userland rootkits.
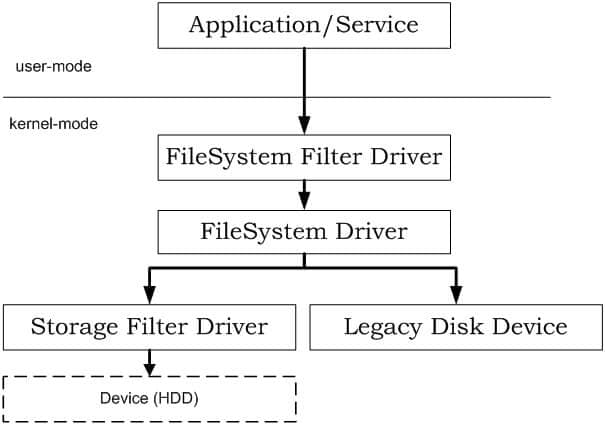
KernelMode Rootkits: Part 3, kernel filters
KernelMode Rootkits explained. This is the third part of this rootkit writing tutorial in which we will detail the basics about kernel rootkits.
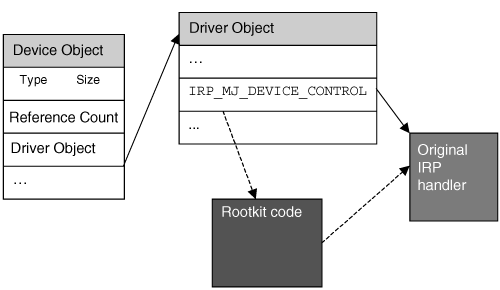
KernelMode Rootkits: Part 2, IRP hooks
KernelMode Rootkits explained. This is the second part of this rootkit writing tutorial in which we will detail the basics about kernel rootkits.
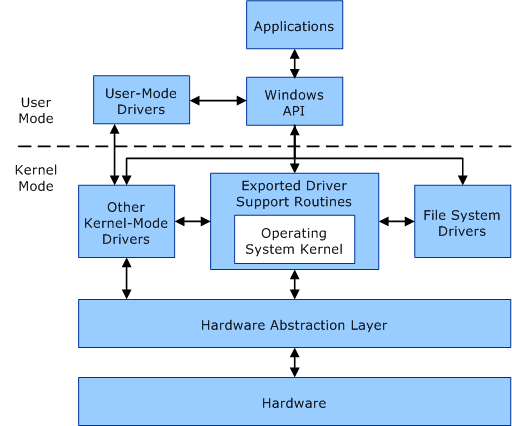
KernelMode Rootkits: Part 1, SSDT hooks
KernelMode Rootkits explained. This is the first part of this rootkit writing tutorial in which we will detail the basics about kernel rootkits.
Facebook Scams: A look behind the scene
You’ve all seen Facebook posts shared by your friends with attractive titles, waiting for you to click. We’ve clicked for you, and you will be deceived.
Symmi Ransomware Decryption
Anlysis of Win32.Symmi Ransomware – Learn how this ransomware encrypts your files, and how to defeat it to decrypt your personal data.
How to Remove Zekos (Guide)
Got infected with Zekos malware? Follow this step by step guide to get rid of it. Our guide also includes a short analysis of the malware.
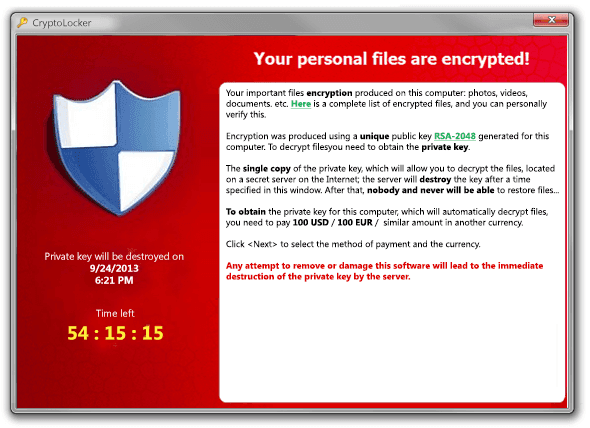
How to Remove CryptoLocker (Guide)
Got infected with CryptoLocker ransomware? Follow this step by step guide to get rid of it. Our guide also includes a short analysis of the malware.
How to Remove Carberp (Guide)
Got infected with Carberp (Zeus/Zbot variant)? Follow this step by step guide to get rid of it. Our guide also includes a short analysis of the malware.
How to Remove ZeroAccess (Guide)
Got infected with ZeroAccess (Sirefef) rootkit? Follow this step by step guide to get rid of it. Our guide also includes a short analysis of the rootkit.

Carberp bootkit : How self-protection is effective
Analysis of the Carberp bootkit capabilities to hide into the system, and self protect its components with a filter driver.

Carberp anti-rapport : Beating Trusteer protection
Carberp Anti Rapport Trusteer – How the Carberp malware is defeating Anti Rapport (from Trusteer) to gain access to the bank account of a victim.