
Introducing: Adlice Labs
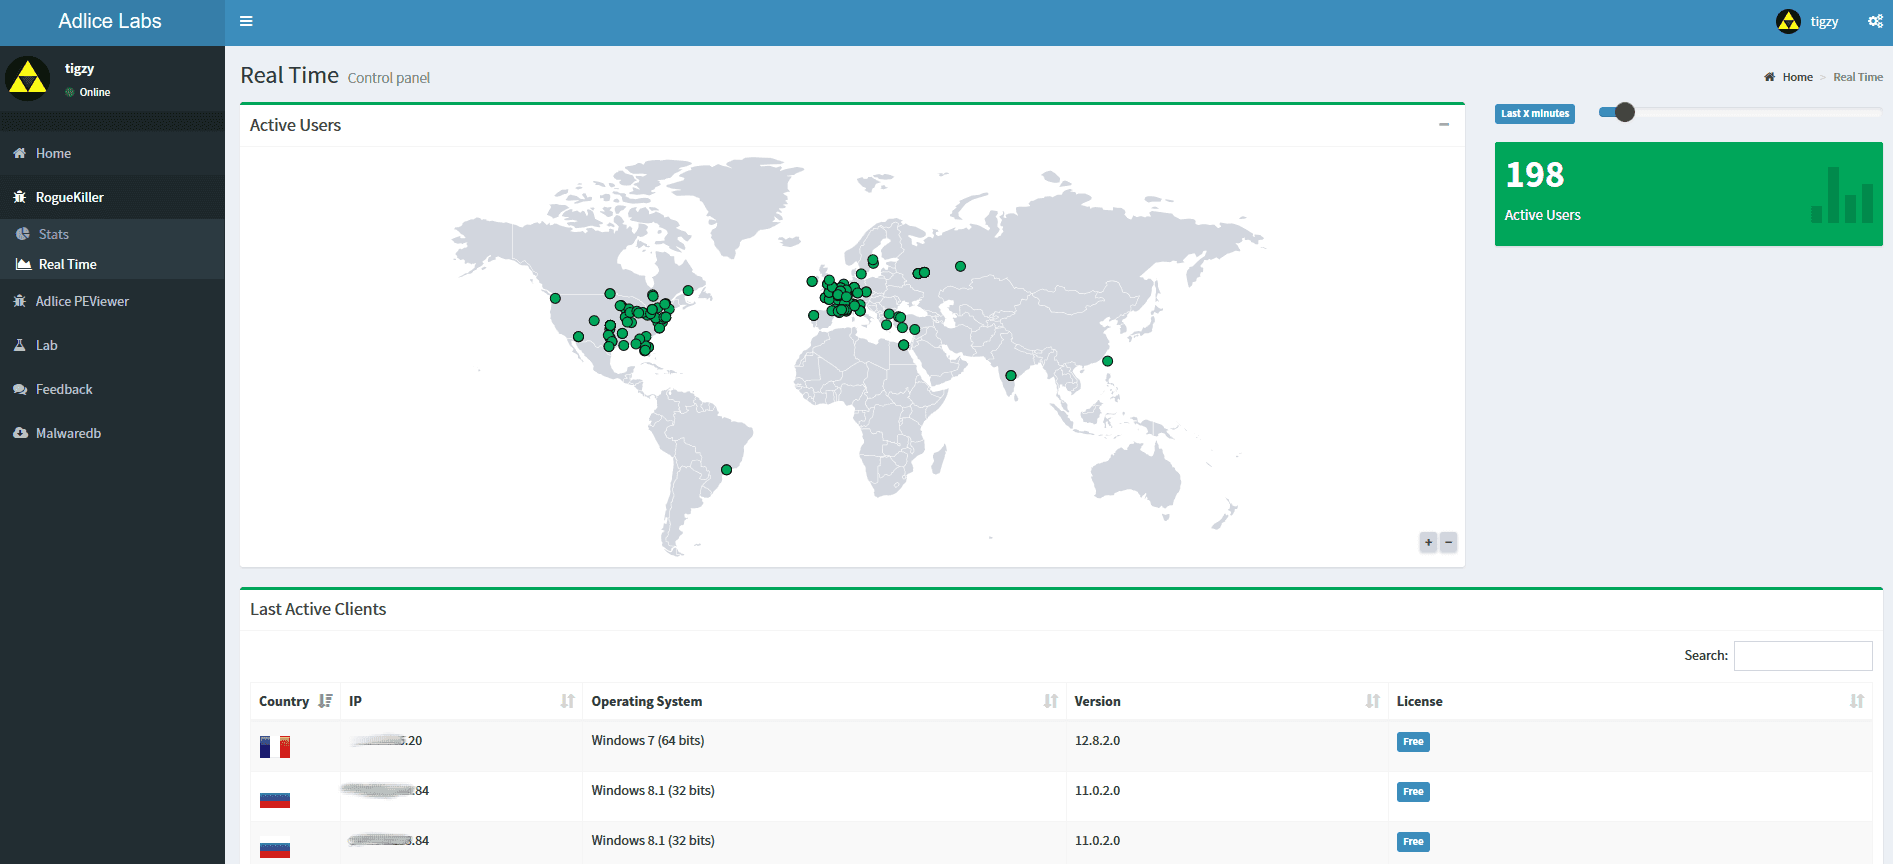
We, at Adlice Software, have started from scratch 5 years ago with a small anti-malware tool called RogueKiller. Now on, we have developed many public and private tools to help researchers and malware analysts in their everyday job, including ourselves. Today, I’m proud to show you the way we work with our brand new Labs, Adlice labs.
Telemetry
Our software are sending telemetry data to help us understanding how many users are using each of them, what are their needs (i.e: translations) and to give us an overview on the popularity of them.
We have developed some dashboards telling us how many scans are performed per day, and also a real-time display of connected users. Note: localizations are not stored in our database, they are in a volatile database, our stored data remain anonymous.
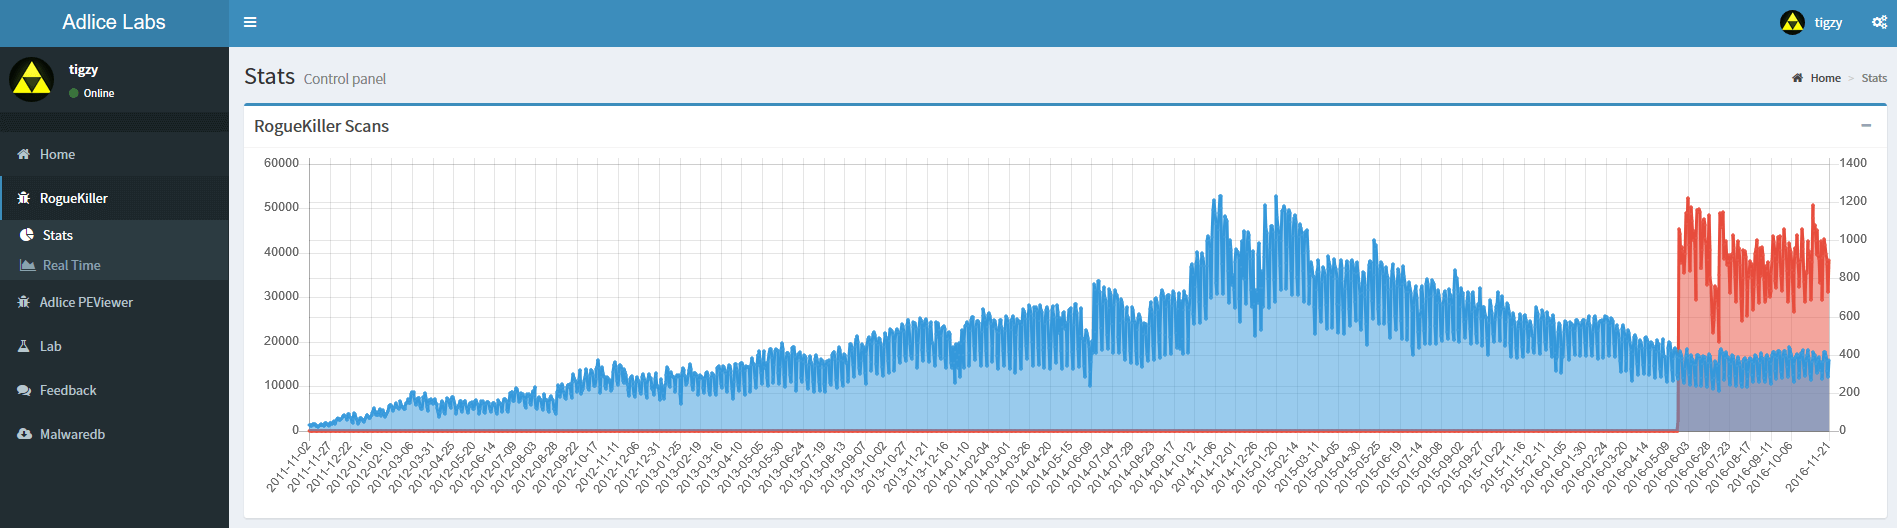 Every day scans
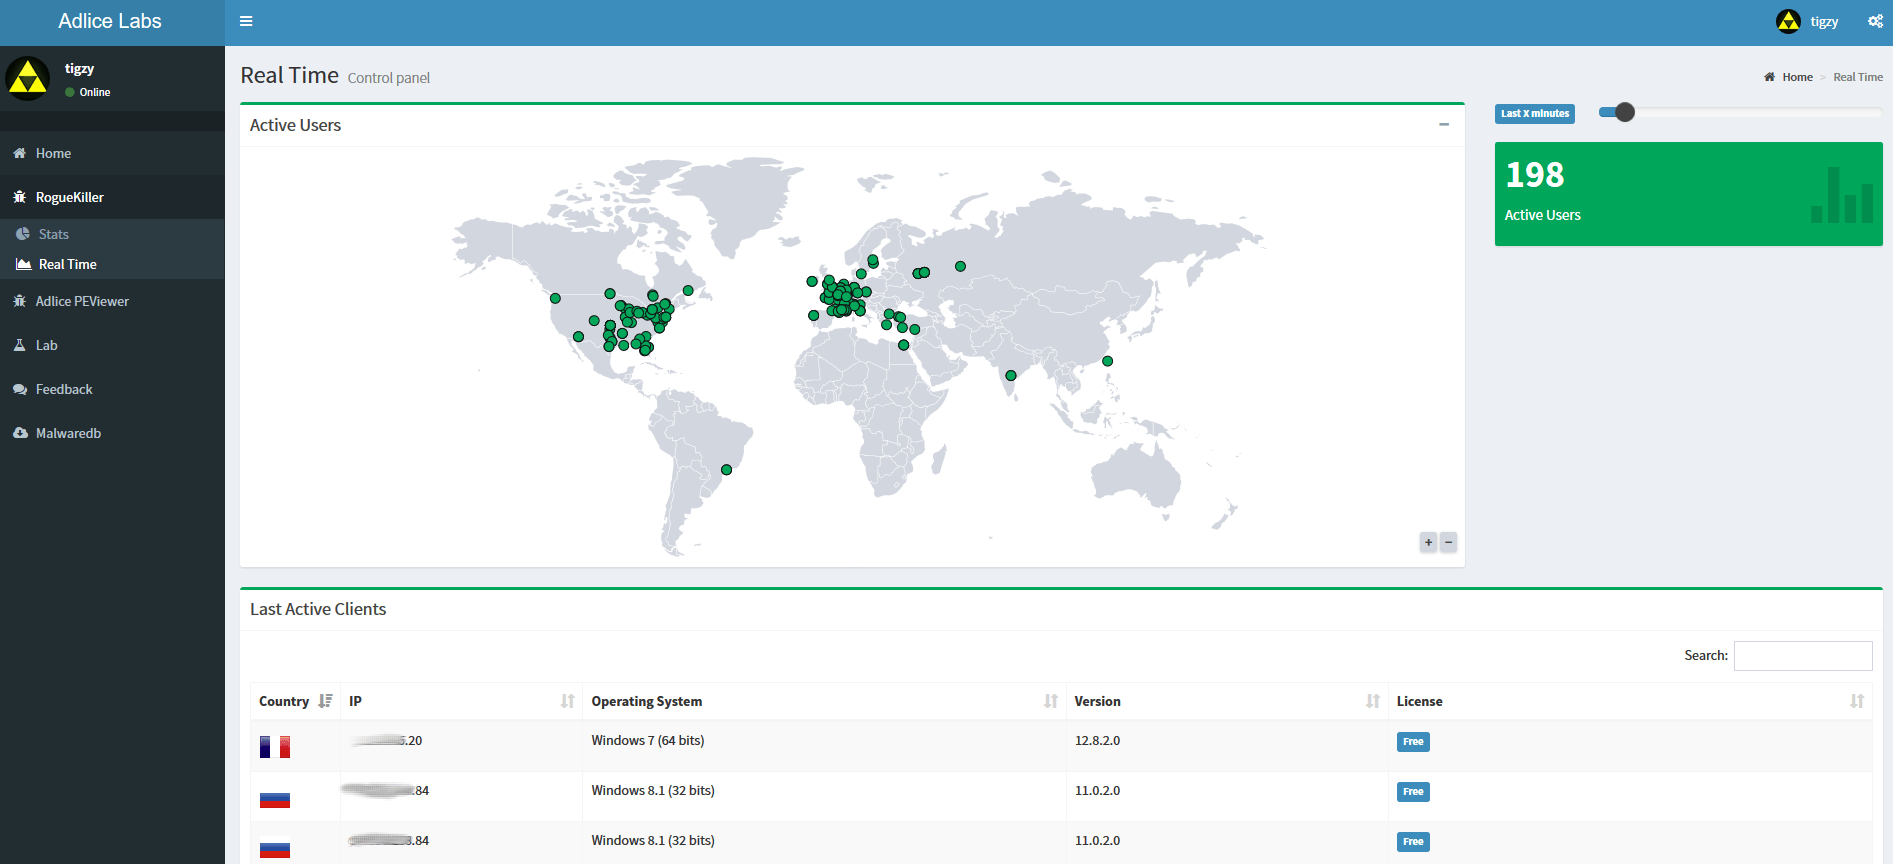 Real-time scans
Automated Signatures
The most interesting part in our labs is the automated classification and prioritization of the detections. When RogueKiller sends back all detections after a scan, everything is put into counted detection items, and sorted so that we can see what the top detections are.
If there are a false positive they can be fixed, if there are heuristic detections they can be formalized into a real signature.
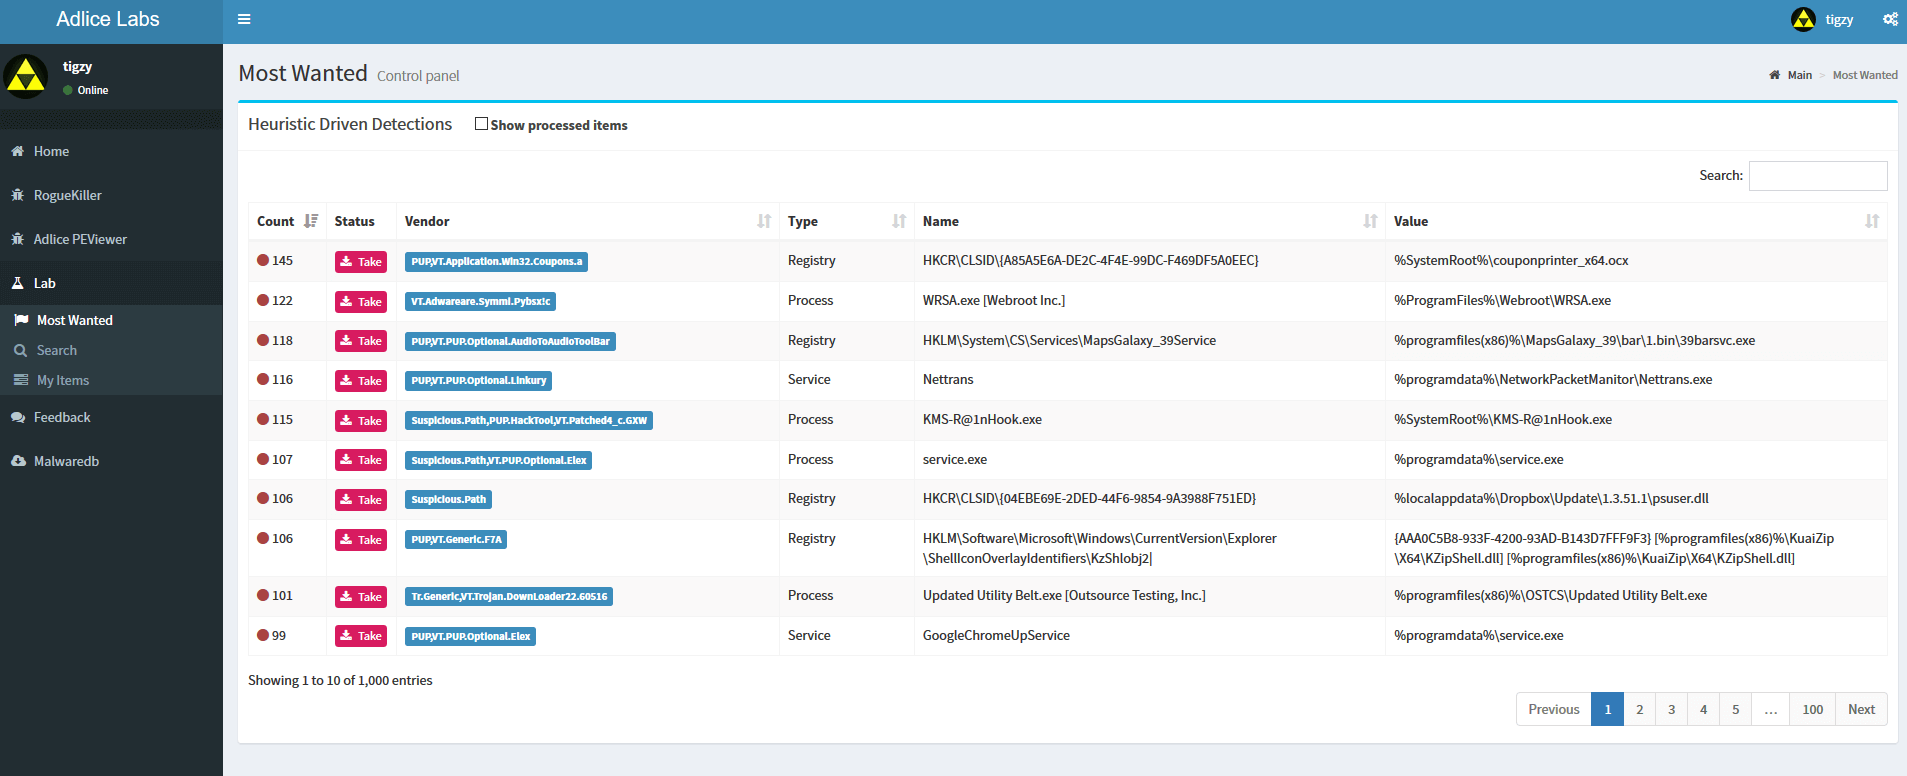 Top Detections
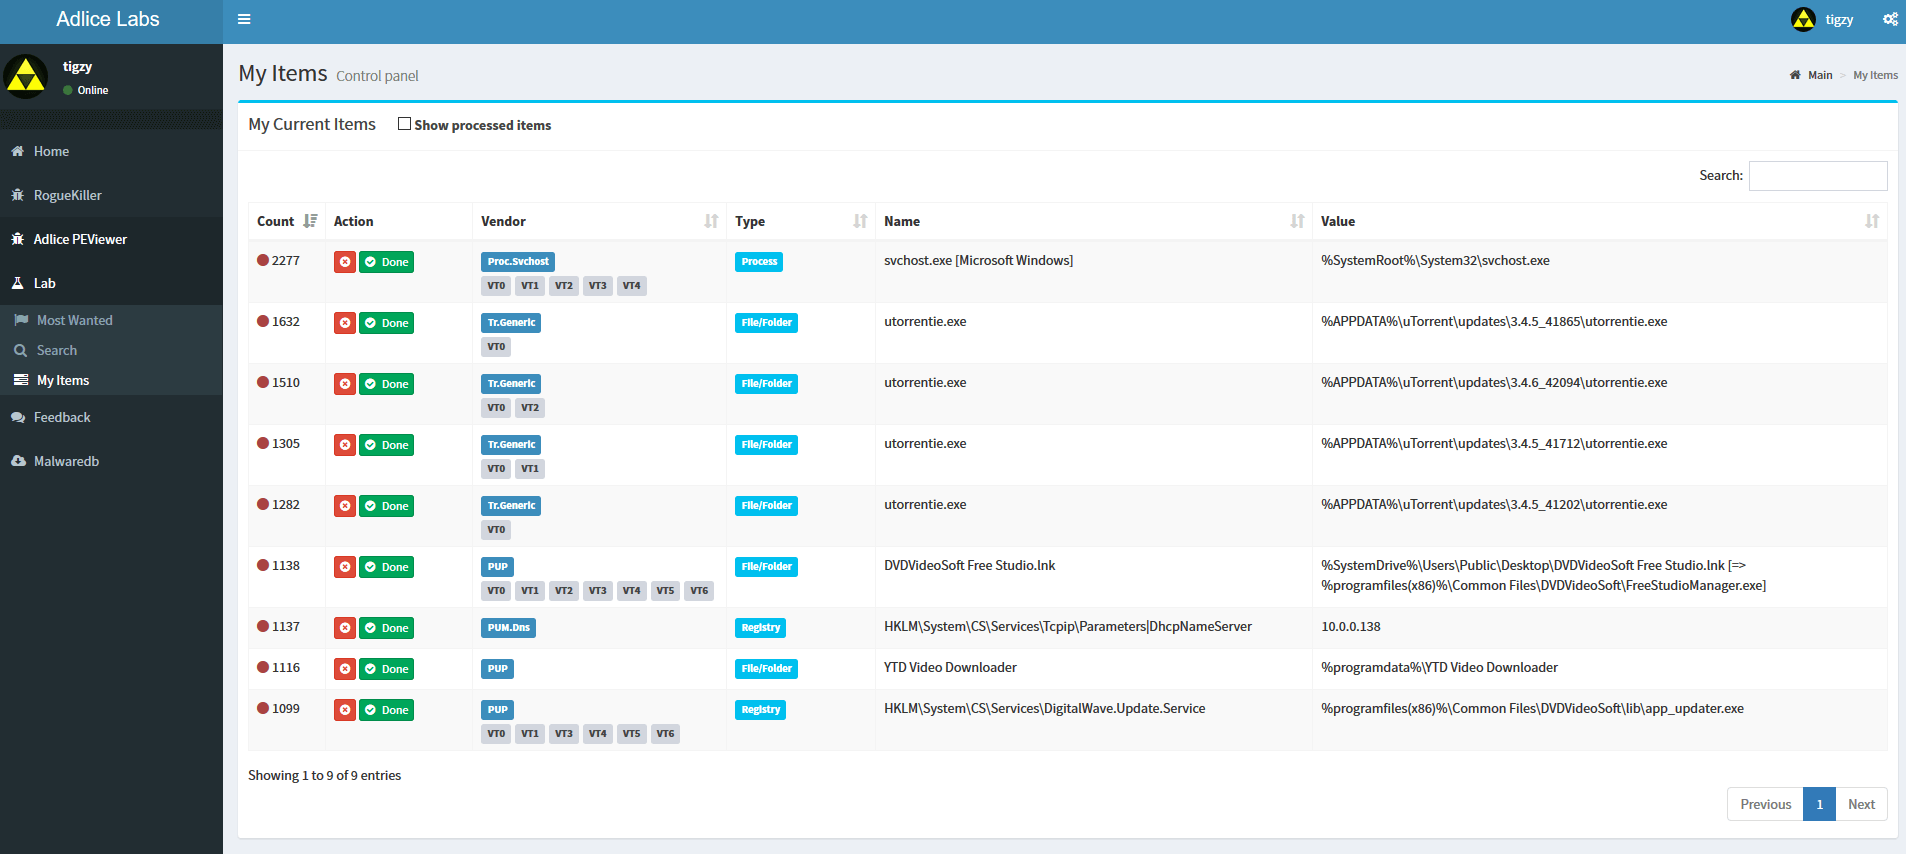 My Items view, used by our researchers to process detection items
Malware Database
Our honeypots and automated scripts are also gathering infectious samples (virus, malware, files) and they are sent into our own MRF database. This helps us to organize the malware we receive in order to analyse them when it’s necessary.
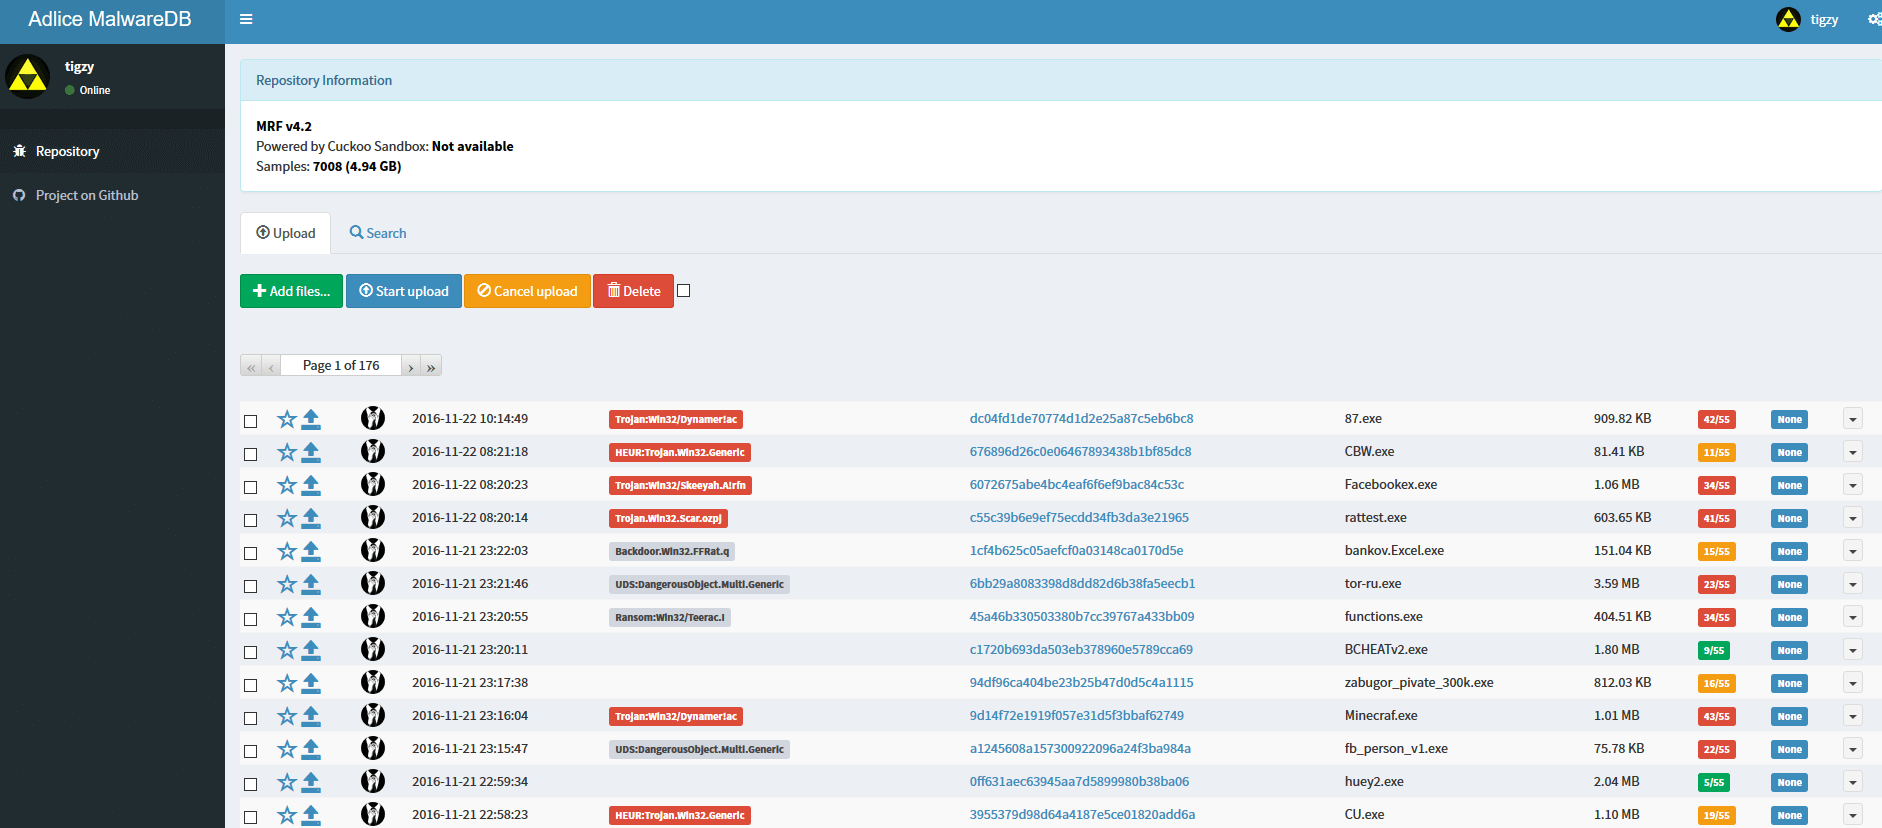 MalwareDB
This new way to work will make our software even more efficient, this is only the beginning !
Thanks a lot for supporting us 🙂