
Configuración
Configuración Bare Metal (opcional)
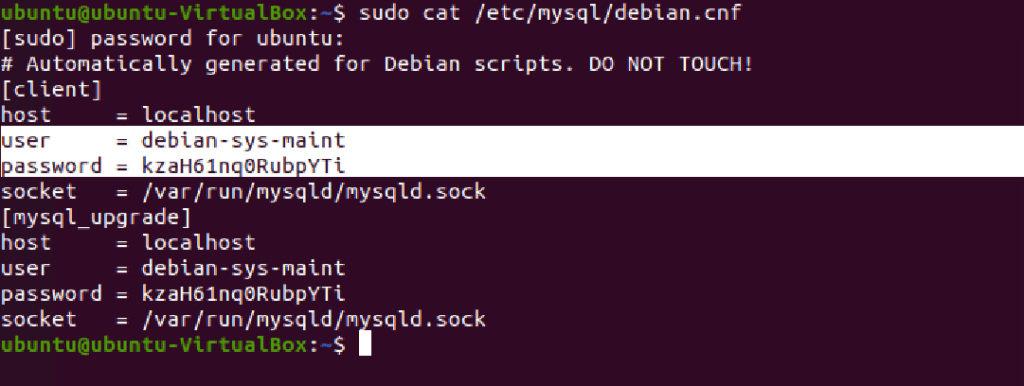
Localice sus credenciales de MySQL. Puede obtenerlas con el siguiente comando.
sudo cat /etc/mysql/debian.cnf
Configuración de Docker (opcional)
No hay que hacer nada específico, salvo lo que ya se hizo en los pasos de instalación.
Simplemente prepare su usuario/contraseña de MYSQL y la ubicación de almacenamiento para los siguientes pasos.
Configuración común
Edite su archivo de configuración (ubicado en /your_root/src/config.php), como se explica a continuación.
A partir de los pasos de instalación, rellene la siguiente información:
- El nombre de la base de datos en las secciones “db/signatures” y “db/usercake”
- Las credenciales de la base de datos (véase más arriba) en las secciones “db/signatures” y “db/usercake”.
- El host de la base de datos en las secciones “db/signatures” y “db/usercake”. NOTA: Para docker debe ser el nombre del contenedor de mysql (“db” en nuestra plantilla).
- Las rutas de almacenamiento en las secciones “tests/storage” y “modules/localstorage/storage” (o configure owncloud si tiene previsto utilizarlo).
- La url pública en la sección “urls/baseUrl”. Ejemplo: “http://localhost” (localmente), “https://my.mrf.example.com/”
Después, modifique el archivo de configuración según sus necesidades (véase más abajo)
Módulos
La mayoría de los módulos no están documentados, no se aconseja cambiar su configuración. Solo unos pocos pueden ajustarse:
Owncloud
- Habilite el módulo con la sección “owncloud/enabled” = True
- Ponga su url de owncloud en la sección “owncloud/url” (véase la documentación de Owncloud)
- Cree una carpeta de almacenamiento en su instancia de owncloud, y ponga su ruta en la sección “owncloud/storage” (ejemplo, “MyFolder”)
- Cree un enlace compartido para esta ubicación de almacenamiento, y póngalo en la sección “owncloud/download_url”. Esto se utilizará para las descargas.
- Ponga sus credenciales de la API de owncloud en las secciones “owncloud/account” y “owncloud/token”. Es preferible crear una clave de API que utilizar contraseñas.
- No olvide volver a ejecutar el script de instalación si es necesario después de cambiar esto
MRF
- Habilite el módulo con la sección “mrf/enabled” = True
- Ponga su url de MRF en la sección “mrf/base_url”
- Ponga su clave de API de MRF en la sección “mrf/api_key”
- No olvide volver a ejecutar el script de instalación si es necesario después de cambiar esto
A continuación encontrará una plantilla de archivo de configuración con opciones preconfiguradas.
No dude en utilizarla como punto de partida.
mostrar plantilla de configuración
<?php

/*
    The important thing to realize is that the config file should be included in every
    page of your project, or at least any page you want access to these settings.
    This allows you to confidently use these settings throughout a project because
    if something changes such as your database credentials, or a path to a specific resource,
    you'll only need to update it here.
*/

$config = array(
    "version" => "1.1",
    "db" => array(
        "usercake" => array(
            "dbname" => "yed",      				// {{CHANGE THIS}} database name for users storage
            "username" => "your_mysql_user",   		// {{CHANGE THIS}} database user for users storage
            "password" => "your_mysql_password",    // {{CHANGE THIS}} database user password for users storage
            "host" => "localhost"   		        // {{CHANGE THIS}} database host for users storage
        ),
        "signatures" => array(
            "dbname" => "mrf",      				// {{CHANGE THIS}} database name for signatures storage
            "username" => "your_mysql_user",   		// {{CHANGE THIS}} database user for signatures storage
            "password" => "your_mysql_password",    // {{CHANGE THIS}} database user password for signatures storage
            "host" => "localhost"   		        // {{CHANGE THIS}} database host for signatures storage
        ),
    ),
    "urls" => array(
        "baseUrl" => "https://yourwebsite.com/" // {{CHANGE THIS}} Base url of your website, TRAILING SLASH NEEDED
    ),
    "ui" => array(
        "template" => "ampleadmin",
        "colors" => "red-dark",
        "is_dark" => True,
    ),

    "yara_version" => "3.11.0",           // {{CHANGE THIS}} (optional) Yara engine version (Python module)
    "cookie" => "yaraeditor",
    "mode" => "workflow",			      // {{CHANGE THIS}} (optional): "workflow" is default, needs approval for rules. "public" does not need approval.
    "leftnav" => array(
    	array(
            "name" => "Dashboard",
            "link" => "/index.php",
            "icon" => "fa fa-dashboard",
        ),
    	array(
    		"name" => "Edition",
    		"icon" => "fa fa-pencil",
    		"link" =>
    		array(
		        array(
		            "name" => "Create",
		            "link" => "/edit.php",
		            "icon" => "fa fa-pencil",
		        ),
    			array(
		            "name" => "My Work",
		            "link" => "/myrules.php",
		            "icon" => "fa fa-flask",
		        )
		    )
    	),
    	array(
    		"name" => "Live",
    		"icon" => "fa fa-industry",
    		"link" =>
    		array(
    			array(
		            "name" => "Files",
		            "link" => "/files.php",
		            "icon" => "fa fa-list",
		        ),
    			array(
		            "name" => "Search",
		            "link" => "/search.php",
		            "icon" => "fa fa-search",
		        ),
				array(
		            "name" => "History",
		            "link" => "/history.php",
		            "icon" => "fa fa-history",
		        ),
    			array(
		            "name" => "Recycle Bin",
		            "link" => "/recycle.php",
		            "icon" => "fa fa-trash",
		        ),
		    )
    	),
    	array(
    		"name" => "Tests",
    		"icon" => "fa fa-refresh",
    		"link" =>
    		array(
    			array(
		            "name" => "List",
		            "link" => "/tests.php",
		            "icon" => "fa fa-list",
		        ),
		    )
    	),
		array(
    		"name" => "Threats",
    		"icon" => "fa fa-bug",
    		"link" =>
    		array(
    			array(
		            "name" => "List",
		            "link" => "/threats.php",
		            "icon" => "fa fa-list",
		        ),
		    )
    	),
        array(
            "name" => "Aliases",
            "icon" => "fa fa-arrow-right",
            "link" =>
            array(
                array(
                    "name" => "List",
                    "link" => "/aliases.php",
                    "icon" => "fa fa-list",
                ),
            )
        ),
		array(
    		"name" => "Publications",
    		"icon" => "fa fa-globe",
    		"link" =>
    		array(
    			array(
		            "name" => "List",
		            "link" => "/publications.php",
		            "icon" => "fa fa-list",
		        ),
		    )
    	),
    ),
    "user_settings" => array(
      "email_notifications" => array(
          "display" => "Email Notifications",
          "settings" => array(
              "new_publication" => array(
                  "name" => "email_notification_on_publication",
                  "display" => "Email notification on new publication",
                  "default" => False
              )
          )
      )
    ),
    "modules" => array(
        "localstorage" => array(
			"enabled" => True,                         			// {{CHANGE THIS}} (optional) Default (local) storage for publication. False to turn it off if you use owncloud
			"class" => "LocalStorage",
			"priority" => 10,
			"storage" => "/data/your_storage_location_here/",   // {{CHANGE THIS}} (optional) Storage location of your publications
			"cron" => True,
		),
        "owncloud" => array(
            "enabled" => False,									// {{CHANGE THIS}} (optional) Owncloud (cloud) storage for publications. True to turn it on, do not forget to turn off localstorage.
            "class" => "Owncloud",
            "priority" => 10,
            "url" => "https://your_own_cloud.com",				// {{CHANGE THIS}} (optional) Owncloud root url
            "download_url" => "https://your_own_cloud.com/index.php/s/share_key",  // {{CHANGE THIS}} (optional) Public link on the root folder (storage location below)
            "storage" => "Storage.Folder.For.Signatures",                          // {{CHANGE THIS}} (optional) Create public link above on this storage folder
            "account" => "username",							// {{CHANGE THIS}} (optional) Your owncloud user
            "token" => "apikey",								// {{CHANGE THIS}} (optional) Your owncloud user API key
            "cron" => True,
        ),
        "mrf" => array(
            "enabled" => False,									// {{CHANGE THIS}} (optional) MRF module, to use tests on real samples stored in MRF. True to turn it on
            "class" => "MRF",
            "priority" => 8,
            "base_url" => "https://yourmrf.com/",				// {{CHANGE THIS}} (optional) Your MRF server location (do not forget last slash)
            "api_key" => ""										// {{CHANGE THIS}} (optional) Your MRF api key
        ),
        "yaradata" => array(
            "enabled" => True,
            "class" => "YaraData",
            "priority" => 9,
            "scanfile_virtual_file_to_use" => => array( "signatures" )	// {{CHANGE THIS}} (optional) The virtual file(s) that will be used to scan with scanfile API
        ),
        "twitter" => array(
            "enabled" => False,				        			// {{CHANGE THIS}} (optional) Post on Twitter when new publication is done
            "class" => "Twitter",
            "priority" => 9,
            "token" => array(
                "consumer_key" => "",							// {{CHANGE THIS}} (optional) Twitter API
                "consumer_secret" => "",						// {{CHANGE THIS}} (optional) Twitter API
                "access_token_key" => "",						// {{CHANGE THIS}} (optional) Twitter API
                "access_token_secret" => ""						// {{CHANGE THIS}} (optional) Twitter API
            ),
            "templates" => array(
                "new_publication" => "New malware #signatures package published (version %%VERSION%%)"	// {{CHANGE THIS}} (optional) template message to use when posting
            )
        ),
        "alias" => array(
            "enabled" => True,
            "class" => "Alias",
            "priority" => 9,
        ),
	),
    "tests" => array(
        "storage" => "/data/your-files-storage/"			// {{CHANGE THIS}} Where to store files uploaded for tests
    ),
    "publication" => array(
		"generate_unencrypted" => True,						// {{CHANGE THIS}} (optional) Generate unencrypted publication package (compiled only)
        "generate_encrypted" => False,						// {{CHANGE THIS}} (optional) Generate encrypted publication package (compiled + xored)
        "encryption_key" => ""								// {{CHANGE THIS}} (optional) Xor key used to encrypt the compiled files. Client must use the same key to use the files

    ),
	"available_imports" => array(
		"pe","elf","cuckoo","magic","hash","math"
	),
	"threats" => array(
	    "goodware_default" => "Safe",
		"types" => array(
			"Safe", "Malware", "Adware", "Ransomware", "Miner", "Trojan", "Rogue", "Keylogger", "Virus", "Rootkit", "Spyware", "Exploit", "Unwanted"
		),
		"platforms" => array(
			"Windows", "MacOSX", "Linux"
		),
	    "mapping" => array(
	        "Safe" => array("filter" => array("Safe."), "criticality" => 1),
	        "Adware" => array("filter" => array("Adw."), "criticality" => 2),
	        "Ransomware" => array("filter" => array("Ransom."), "criticality" => 3),
	        "Miner" => array("filter" => array("Miner.","BitMiner."), "criticality" => 3),
	        "Trojan" => array("filter" => array("Tr."), "criticality" => 3),
			"Unwanted" => array("filter" => array("PUP.", "PUM."), "criticality" => 2),
	        "Rogue" => array("filter" => array("Rogue."), "criticality" => 3),
	        "Keylogger" => array("filter" => array("Keylog."), "criticality" => 3),
	        "Virus" => array("filter" => array("Vir."), "criticality" => 3),
	        "Rootkit" => array("filter" => array("Root."), "criticality" => 3),
	        "Spyware" => array("filter" => array("Spy."), "criticality" => 3),
	        "Exploit" => array("filter" => array("Exploit."), "criticality" => 3),
	    )
	),
    "misc" => array(
        "confirm_rule_submit" => False					// {{CHANGE THIS}} (optional) Display popup to confirm rule submission
    ),
    "cron" => array(
        "enabled" => False
    ),
);

$GLOBALS["config"] = $config;

// Conditional config
if ($config["mode"] !== "public") {
    array_splice($config["leftnav"][1]["link"], 2, 0, array(array(
        "name" => "Approval",
        "link" => "/approval.php",
        "icon" => "fa fa-thumbs-up",
        "access" => ["admin","publisher","manager"]
    )));
}

// Init globals
// We put this code in config so that it's called on every php page
require_once(__DIR__."/lib/usercake/init.php");
$user = UCUser::getCurrentUser();

require_once(__DIR__."/core.php");
YEdCore::LoadUserGlobalPermissions();

function IsModuleEnabled($module) {
    return isset($GLOBALS["config"]["modules"][$module]) && $GLOBALS["config"]["modules"][$module]["enabled"];
}

/*
    I will usually place the following in a bootstrap file or some type of environment
    setup file (code that is run at the start of every page request), but they work
    just as well in your config file if it's in php (some alternatives to php are xml or ini files).
*/

/*
    Creating constants for heavily used paths makes things a lot easier.
    ex. require_once(LIBRARY_PATH . "Paginator.php")
*/
//defined("LIBRARY_PATH")
//    or define("LIBRARY_PATH", realpath(dirname(__FILE__) . '/library'));

//defined("TEMPLATES_PATH")
//    or define("TEMPLATES_PATH", realpath(dirname(__FILE__) . '/templates'));

/*
    Error reporting.
*/
ini_set("error_reporting", "true");
error_reporting(E_ALL|E_STRCT);

?>
ocultar plantilla de configuración